

An ANNUAL SECURITY EVENT FOR THE LOW COUNTRY
Why BSides Charleston?
A combination of students, professionals, geeks, and tinkerers gathering to discuss Information Security, hear awesome talks, and bring security into our everyday lives. Our mission is to provide an inclusive, inspiring, and motivational environment to discuss and collaborate on information security and how it inspires, interests, and motivates you. This will almost a decade of BSides in Charleston. With the eclectic businesses and people from the Lowcountry, we expect to have an outstanding event that will be fun, educational, and inspirational for all. Follow us on twitter @BSidesCHS to keep up with the latest information.

Schedule of Events
Workshops
& Demos
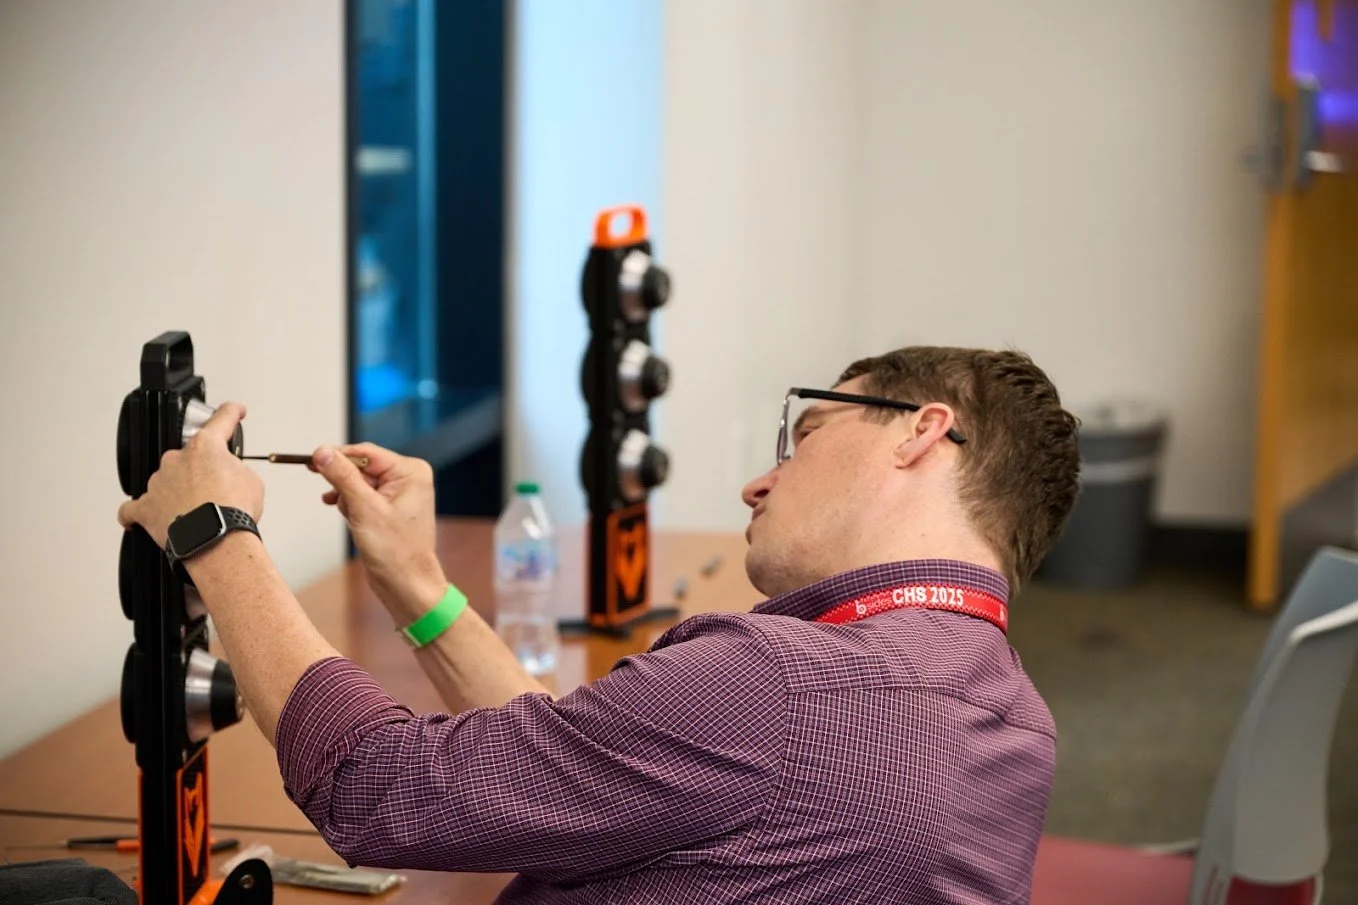
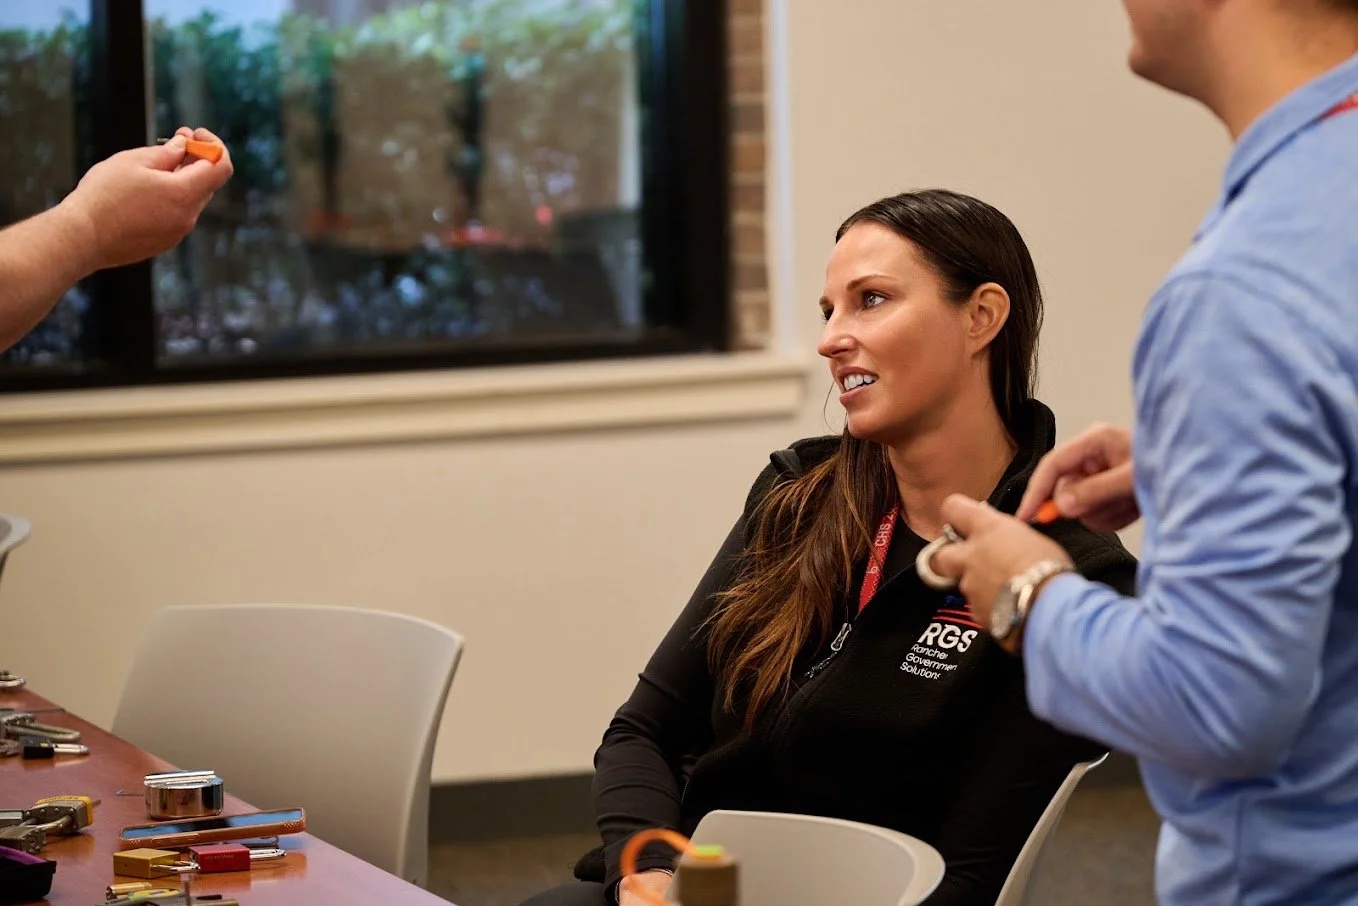
During BSides Charleston the community has an opportunity to attend free training sessions on a variety of information security topics. Seats in these sessions are reserved by sign up prior to the conference day. All free training sessions are typically scheduled the day before the conference talks.
2026 Workshops
Friday, November 6, 2025 | 5:30pm - 8:30pm
College of Charleston - Beatty Cent4er
5 Liberty Street
Charleston, SC 29424
BSides CHS Training: BBOT - Bighuge BLS OSINT Tool w/ Black Lantern Security
Reconnaissance is the foundation of every successful engagement, but fragmented tooling, manual chaining, and missed data leave gaps that cost you findings. BBOT (Bighuge BLS OSINT Tool) was built to solve that. Developed by Black Lantern Security, BBOT is a recursive, event-driven OSINT framework that replaces the traditional phased approach with continuous, real-time discovery. Every new piece of data is immediately fed back into the scan engine to uncover what linear workflows miss.
This is a fully hands-on workshop. Attendees will install and configure BBOT, then run it live against their own scoped bug bounty targets, turning the session into real reconnaissance rather than a slide-driven demo. We'll cover BBOT's 100+ module architecture spanning subdomain enumeration, cloud asset discovery, email harvesting, web spidering, and vulnerability scanning with Nuclei, all chainable in a single command and firing recursively in real time. Along the way, we'll dig into scope management, passive vs. active recon tradeoffs, and the web hacking modules that can point you toward real findings. By the end of the session, attendees will walk away with actual scan output from a live target, a repeatable BBOT-driven recon workflow they can drop into their next program, and a clear understanding of how to triage findings into real submissions. Whether you're new to automated recon or a seasoned bug bounty hunter still stitching tools together by hand, this workshop will change how you approach OSINT at scale.
BSides CHS Training: Shark Bite: Demystifying Network Traffic w/ Google
Stop Guessing, Start Sniffing: Hands-On Network Traffic Analysis & Incident Triage with Wireshark
When a critical alert hits your SOC, packet analysis shouldn't feel like trying to decode the falling green code in The Matrix. This highly interactive, hands-on workshop is specifically built for junior analysts and security newcomers ready to turn Wireshark into their ultimate incident response superpower.
We will demystify Wireshark's built-in triage tools to save you from "death by data," showing you exactly how to capture, dissect, and confidently interpret raw traffic. You will learn the exact workspace customizations and tricks the pros use to streamline investigations, equipping you with the visual triage skills and packet-level intuition needed to reconstruct complex timelines. Through a balance of theory and interactive lab challenges, you'll hunt for active C2 beaconing, trace malicious reconnaissance, and safely extract payloads.
Key Takeaways & Discussion Topics
Following the Stream: Understand TCP/UDP stream reconstruction, and navigate the practical limitations of encrypted HTTPS traffic during an investigation.
Rapid Triage via Statistics: Leverage Protocol Hierarchies, Conversations, and Endpoints to identify anomalous behaviors in seconds.
Precision Display Filters: Master display filter syntax and identify common pitfalls that lead to missed packet data.
Artifact & Object Extraction: Safely carve out objects and payloads from packet captures using best practices.

This could not happen
without help from our:
Sponsors
The goal of BSides is to offer small intimate events where all participants can engage each other to help develop connections and friendships, and network with different industry professionals. We would not do without our sponsors who allow us to provide shirts, signage/lanyards, lunch sessions, and badges to attendees each year.
Thank you to our 2026 Sponsors!

Location
Charleston, SC
Beatty Center - College of Charleston
5 Liberty Street
Charleston, SC 29424

Beatty Center - College of Charleston School of Business
“What hackers do is figure out technology and experiment with it in ways many people never imagined. They also have a strong desire to share this information with others and to explain it to people whose only qualification may be the desire to learn.”
